 Secure
Are You Taking These 7 Steps to Prevent Ransomware?
Ransomware saw a disturbingly significant increase in both popularity and impact in 2020.


Written by the engineers who do the work: practical security, compliance, resilience and AI advice. When something in an older post has changed, an editor's note says so.
SecureRansomware saw a disturbingly significant increase in both popularity and impact in 2020.
 Culture · Secure
I lead NorthState’s Technology team, responsible for the networking, systems, business applications and security on which our company and customers depend.
 Secure
If you are new to the series please start with Day 1 . If not, welcome back!
 Compliant
A counter to fear-driven CMMC marketing. Kyl frames compliance as a set of habits, illustrated with haiku about protecting CUI and MFA prompts, and calls for a clear plan instead of panic.
 Technical library · Dependable
Sync a local folder to SharePoint without robocopy or scheduled tasks: make the OneDrive folder the source and point a symbolic link at it.
 Compliant
CMMC Phase II assessments were suspended, but DFARS 7012 still requires NIST 800-171, SPRS scores and honest affirmations.
 Compliant
Kyl examines the DoD CIO's voluntary "Brilliant at the Basics" lists, published alongside the CMMC pause, which bring back practices removed in the move to CMMC 2.0. He notes the tension between relieving cost burden and the reappearing expectations.
 Compliant
While attention is on CMMC, the Revolutionary FAR Overhaul may renumber every Part 52 provision and clause, which would break clause matrices and templates. Kyl notes that FAR 52.204-21's 15 FCI controls overlap with CMMC Level 1 without being the same obligation, and that public comment is open.
 Compliant
A week after the CMMC Phase 2 suspension, Kyl describes a defense industrial base split between relief and alarm, and urges contractors to answer the DoW RFI by August 14, 2026. Meanwhile NIST 800-171 and DFARS 7012 obligations still apply.
 Compliant
Kyl argues that confusing federal data and contract terms (FCI, CUI, ITAR, EAR, FAR, DFARS) can end a contract. The terms overlap but aren't interchangeable, and the post links to a plain-English breakdown of all six.
 Dependable
I’ve been consulting for about the last 18+ years and have worked with dozens of organizations of all sizes, shapes and even nationalities.
 Secure
Hello! If you are new to the series make sure to check out Day 1 .
 Secure
Hello! If you are new to this series on securing your small business in 5 minutes per day than you should start with Day 1 .
 Secure
Day 2: if you are new to this series please start with Day 1 If you are returning, welcome back! So you have pulled together a list of your digital assets, applications and systems...now what to do with the list.
 Secure
To get right to it skip the first paragraph... This is the start of a simple mission to reveal, in plain language, the actions you can take to protect your business.
Grouped by topic, with our most useful current advice first in each. An editor's note flags anything that has changed since a post was written.
 Secure
Pragmatic security advice balances risk, usability and cost. “Tin foil hat” advice chases unlikely threats. How to tell the difference.
 Secure
Why a penetration test is to security what an audit is to your finances, what a real manual test includes, and how to choose a firm.
 Secure
How a man-in-the-middle phishing page steals a password and an MFA approval in real time, and the controls that stop it.
 Secure
Should you force password changes every 90 days? How long should passwords be? Our answers, based on NIST guidance.
 Secure
Build security awareness training around your real risks: key topics, phishing simulations, leadership buy-in, role-based content and measured results.
 Secure
Phishing, weak or stolen passwords and unpatched systems cause most small business breaches. How to prevent each one.
 Secure
Popular wisdom, the news, personal bias or a trusted vendor: four common ways security budgets get spent, and why data-driven risk modeling beats all four.
 Secure
A client paid for a penetration test and got a vulnerability scan. Why security service names are so loose, and what buyers should ask before they sign.
 Secure
Day 1 of our small business security series: spend 5 minutes listing every digital platform, account and device your business relies on.
 Secure
Day 2 of our small business security series: clean up your list of digital assets and delete the accounts, apps and services you no longer use.
 Secure
Day 3 of our small business security series: rank each digital asset by how much harm its loss or exposure would cause your business.
 Secure
Day 4 of our small business security series: data you keep is a risk as well as an asset. What to wipe, delete or encrypt first.
 Secure
Day 5 of our small business security series: check that workstation, server, network and home-office firewalls are turned on and set correctly.
 Secure
Day 6 of our small business security series: review who can access each digital asset, and remove old, duplicate and over-privileged accounts.
 Secure
Day 14 of our small business security series: find equipment past its end-of-life date, record it, and replace what no longer gets security updates.
 Secure
Day 15 of our small business security series: short, regular training and simulated phishing give the best return for most small businesses.
 Secure
Howdy, if you are new to this series start with past me on Day 1 ! For the rest of you...you are stuck with present me.
SecureDay 2: if you are new to this series please start with Day 1 If you are returning, welcome back! So you have pulled together a list of your digital assets, applications and systems...now what to do with the list.
 Secure
If you are new to the series please start with Day 1 . If not, welcome back!
 Secure
Hello! If you are new to this series please start with Day 1 or if you missed any other days they can all be found Here .
SecureHello! If you are new to this series on securing your small business in 5 minutes per day than you should start with Day 1 .
SecureHello! If you are new to the series make sure to check out Day 1 .
 Secure
Howdy, if you are new to the series start here . If you are caught up, welcome back!
 Secure
Salutations, if you are new to the series start here Day 1 . To those who are caught up let's get to it.
 Secure
Hello! If you are new to this series please start with Day 1 .
 Secure
Hail! If you are new to the series start with Day 1 .
 Secure
Hello! If you are new to the series start with Day 1 .
 Secure
Ransomware saw a disturbingly significant increase in both popularity and impact in 2020.
 Secure
Hello! If you are new to this series start with Day 1 .
 Secure
Howdy! If you are new to the series start with Day 1 .
 Secure
Welcome, if you are new to the series start with Day 1 . For those who are all caught up let's continue.
SecureTo get right to it skip the first paragraph... This is the start of a simple mission to reveal, in plain language, the actions you can take to protect your business.
 Secure
Salutations! If you are new to the series start with Day 1 .
 Dependable
Intimidation, budget, the tyranny of the urgent and “we’re too small”: why continuity plans stall, and free help with three of the four.
 Dependable
Stuck with a mediocre MSP because switching costs too much? Three ways to protect yourself: financial accountability, third-party audits, real references.
 Dependable
An archived snapshot of ransomware statistics: costs, attack vectors, downtime, insurance, healthcare and crypto. The figures are historical.
DependableI’ve been consulting for about the last 18+ years and have worked with dozens of organizations of all sizes, shapes and even nationalities.
 Compliant
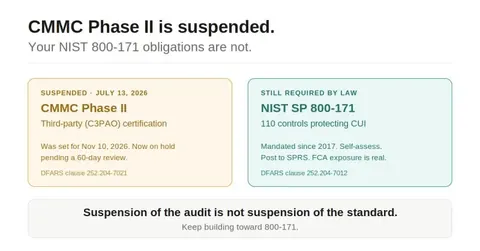
CMMC Phase II assessments were suspended, but DFARS 7012 still requires NIST 800-171, SPRS scores and honest affirmations.
 Compliant
Proprietary data, FCI and CUI nest like Russian dolls. Three questions to tell which you hold, and which rulebook (FAR, DFARS, ITAR or EAR) applies.
 Compliant
What ITAR is, what the US Munitions List covers, what counts as an export, and how to tell whether your business must comply.
CompliantA week after the CMMC Phase 2 suspension, Kyl describes a defense industrial base split between relief and alarm, and urges contractors to answer the DoW RFI by August 14, 2026. Meanwhile NIST 800-171 and DFARS 7012 obligations still apply.
 Compliant
On the July 13, 2026 suspension of CMMC Phase II, Kyl explains that only the DFARS 7021 certification gate is paused. DFARS 7012, which requires NIST 800-171, and the SPRS self-assessment duties still apply, and a proposed FAR CUI rule could widen 800-171.
CompliantWhile attention is on CMMC, the Revolutionary FAR Overhaul may renumber every Part 52 provision and clause, which would break clause matrices and templates. Kyl notes that FAR 52.204-21's 15 FCI controls overlap with CMMC Level 1 without being the same obligation, and that public comment is open.
CompliantKyl examines the DoD CIO's voluntary "Brilliant at the Basics" lists, published alongside the CMMC pause, which bring back practices removed in the move to CMMC 2.0. He notes the tension between relieving cost burden and the reappearing expectations.
CompliantKyl argues that confusing federal data and contract terms (FCI, CUI, ITAR, EAR, FAR, DFARS) can end a contract. The terms overlap but aren't interchangeable, and the post links to a plain-English breakdown of all six.
 Compliant
A counter to fear-driven CMMC marketing. Kyl frames compliance as a set of habits, illustrated with haiku about protecting CUI and MFA prompts, and calls for a clear plan instead of panic.
 Relevant
A date bug that only appeared in Azure Functions, a test harness that hid it, and how an LLM, after some wrong turns, found the root cause.
 Technical library · Dependable
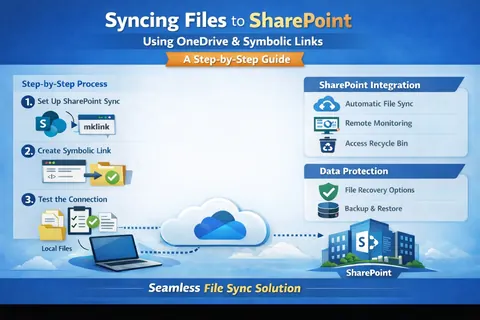
Sync a local folder to SharePoint without robocopy or scheduled tasks: make the OneDrive folder the source and point a symbolic link at it.
 Technical library · Dependable
How an always-on VPN with a pre-logon device tunnel and an MFA-protected user tunnel improves device authentication, user authentication and visibility.
 Technical library · Compliant
CUI and ITAR files should not land in commercial Salesforce. Use lightning-input type=file to send uploads straight to GCC High SharePoint, with code.
 Technical library · Dependable
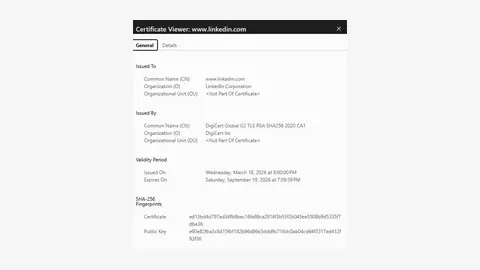
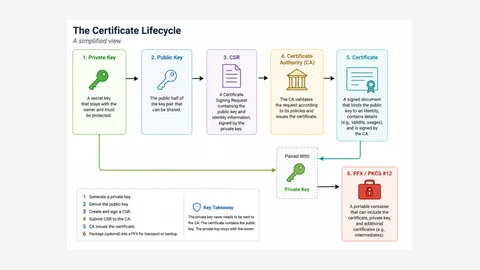
Part One: What is a Certificate, Really? This is going to be the first post of a 10-part series (maybe more) where I break down certificates: what they are, what they do, how they're used, and where trouble might be "creepin' 'round the bend." We're going at this with baby steps first, with a gradual crescendo into the heavier-ish items.
 Technical library · Dependable
Part 2: A Key, or Not a Key? That is the Question.
 Culture · Compliant
Marshall wanted to command D-Day and refused to ask for it. What that taught one of our Principal Engineers about leading to serve, not to be served.
 Culture · Secure
I had the privilege of attending the Executive Symposium @CiscoLive this year. The content was great, and I got to hear a number of highly impactful presentations.
 Culture · Secure
I lead NorthState’s Technology team, responsible for the networking, systems, business applications and security on which our company and customers depend.
 Culture · Secure
I’ve just finished listening to “How to Lead When you’re not in Charge” by Clay Scroggins.
 Culture · Secure
Anyone that manages highly technical resources has gone through the experience of losing a key team member. It’s painful to lose good people and only natural to think in terms of retention strategies.
 Culture · Secure
I’ve had a number of friends and colleagues over the years that will either roll their eyes and/or disengage when someone brings up the subject of ‘corporate culture’.
 Culture · Secure
If you are currently searching for a new job opportunity, LinkedIn can be a valuable resource. With over 722 million users worldwide, LinkedIn offers unparalleled access to professional connections and potential employers.
Got a question one of these posts didn't answer? Ask the engineer who would do the work.
Prefer email? Send us a note instead.